
Safety controls
On top of the always-on governance model, the plugin offers five optional controls. All five stay off until you set them.
Per-minute rate limit
Section titled “Per-minute rate limit”Set a per-minute cap on the Settings tab under “Rate limit (per minute)”. Each agent user can make that many calls a minute, shared by all of that user’s connections; 0 turns the limit off. On the Connection tab you can also give one OAuth connection a lower limit of its own, and its calls count against both. Calls over the cap are denied and logged on the Activity Log tab, so you can spot a connection that keeps hitting it. Since 1.10.1 the refusal tells the agent which limit stopped the call and what that limit is.
IP allowlist
Section titled “IP allowlist”Restrict connections to a list of IP addresses you trust. Off until you set it.
Behind Cloudflare or another proxy, every request arrives from the proxy’s
address, so turn on Real visitor address behind a proxy or CDN
before you list visitor addresses here. Since 1.10.1 a request from an address
that is not on the list gets a 403 with the code aafm_ip_blocked, so the agent
can tell a blocked address apart from a missing permission.
Requests from other web pages
Section titled “Requests from other web pages”This one is not a setting. Since 1.10.1 the MCP endpoint refuses requests sent
from a web page on another site, as the MCP specification requires, with a 403
and the code aafm_origin_not_allowed. The site’s own pages, the hosted ChatGPT
and Claude apps, and desktop and command-line clients, which send no Origin
header, are not affected. Developers can allow a browser client they trust with
the aafm_mcp_allowed_origins filter. Every MCP response also carries
Cache-Control: no-store.
Force-to-draft mode
Section titled “Force-to-draft mode”Hold new posts the agent creates, and any request to publish, as drafts so a human publishes them. It does not hold edits to a post that is already live, so connect the agent as a Contributor if you want those reviewed too. Sending “publish” again for a post that is already live leaves it live.
The Needs review card on the Dashboard lists the drafts and pending posts an agent starts, with Preview, Open in editor, Publish and Discard buttons. Discard moves the post to the Trash, and is unavailable when the Trash is off.
Title-length cap
Section titled “Title-length cap”Cap the length of titles the agent can set, a small guard against runaway or malformed content.
Block-markup validation
Section titled “Block-markup validation”When an agent writes a page, post, template, or reusable block, the plugin steers the styling into block attributes instead of inline CSS and checks the markup before it saves. That keeps agent-authored content from showing up as “invalid content” in the block editor. It warns by default. Turn on strict mode and a block that fails validation is refused rather than saved with a warning.
Since 1.10.0 the warnings also flag unregistered blocks, unknown ACF fields, invalid attribute JSON, ignored block gaps and removed style or script elements. Those are informational and never refuse a write, even in strict mode. The block tools page lists them.
Per-role and per-connection allowlist
Section titled “Per-role and per-connection allowlist”Added in 1.7.4. The abilities you enable on the Abilities tab apply to the whole site. This screen narrows that further, for one role or for one connection.
The rules only ever narrow. An ability has to clear the global list, then the role’s list, then that connection’s list before an agent can call it, so a row here can take reach away and can never add it. That order is enforced twice, once when the agent asks what tools exist and again when it calls one, so a tool it cannot use does not show up in its list either.
A site that never opens the screen sees no change at all. Scoping works at the role level and the connection level. There is no per-Application-Password scoping, so if you need two agents with genuinely different reach, give them separate connections or separate users.
Since 1.7.5 you set this with a searchable checkbox picker rather than by typing ability slugs into a text box, and the role and client fields are selects listing what actually exists on your site. The stored data and the narrowing rules are identical either way; only the input control changed. The same release added a Client ID copy control and paginated the Connection tables.
Since 1.10.0 each OAuth connection can also carry an access preset (Read only, Content editor, Shop manager or Custom), and can be paused or given an end date. A preset narrows on top of these lists and never widens them. See Controlling each connection.
Alerts when something happens
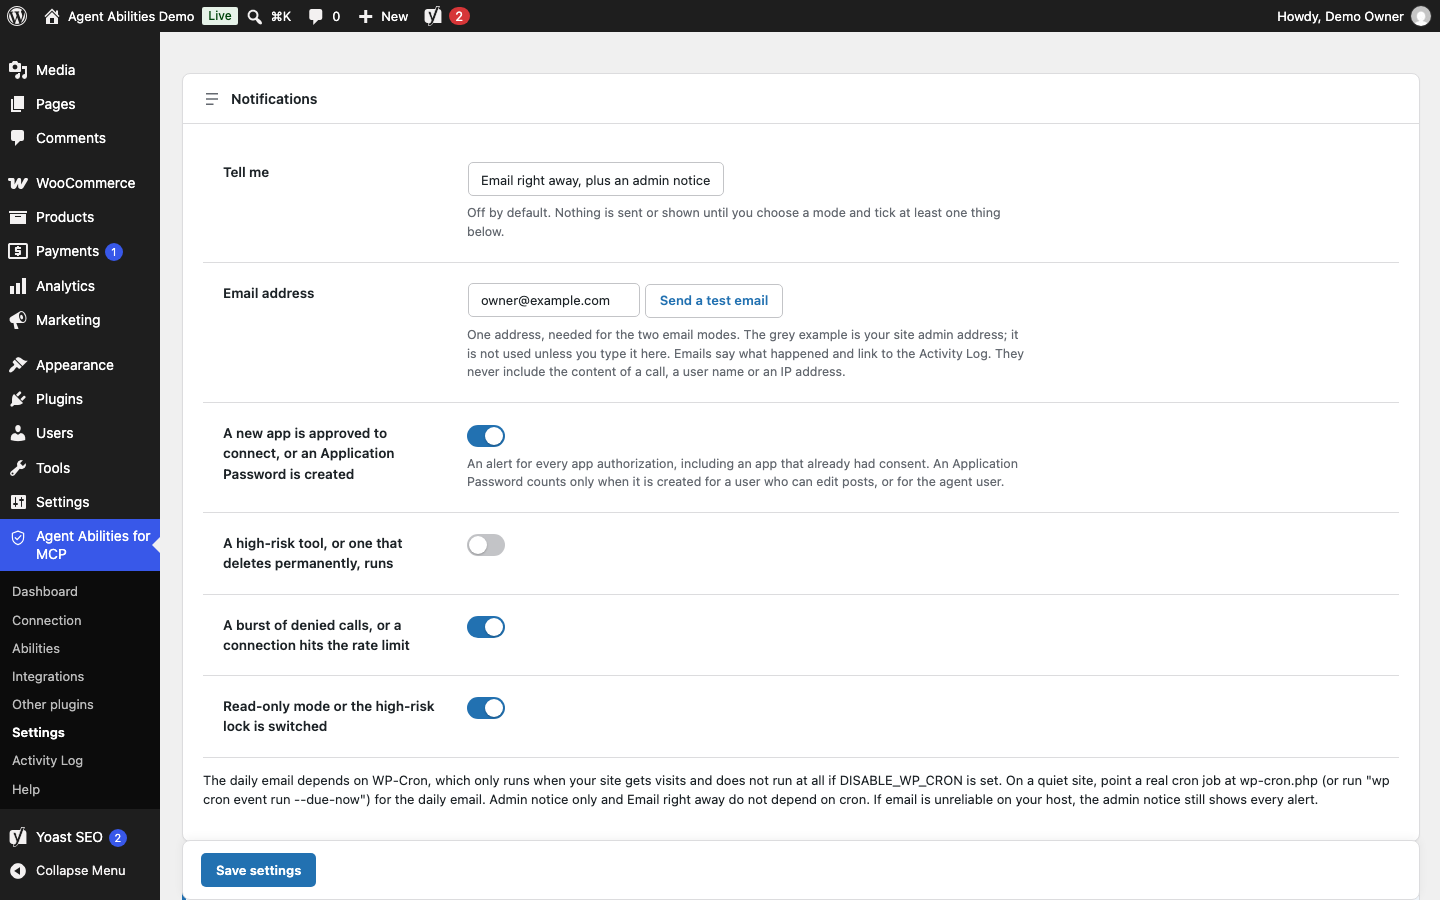
Section titled “Alerts when something happens”Added in 1.9.0, and off by default. The controls above stop things. Alerts tell you about them. Under Settings, Notifications, choose how to be told: “Admin notice only”, “Email right away, plus an admin notice”, or “One email a day, plus an admin notice”. Then tick the events you care about:
- An app is authorized to connect, or an Application Password is created for a user who can edit posts or for the agent user.
- A high-risk tool or a permanent delete runs, including a destructive tool from another plugin.
- Calls are denied in a burst, or a connection hits the rate limit.
- Read-only mode or the high-risk lock is switched on or off.
- Another plugin adds new AI tools. Added in 1.11.0. It tells you to review them and turns nothing on, and the count in the daily email can read low.
Each type of event sends at most one email every 15 minutes, so turning read-only mode on and turning it off count separately. On top of that, four hourly allowances cannot use each other up:
| Allowance | Emails per hour |
|---|---|
| Switch changes, new tools from other plugins, and the warning sent to the previous address when alerts are redirected or weakened | 6 |
| High-risk and permanent-delete runs | 4 |
| New apps and Application Passwords | 2 |
| Denied-call bursts and rate-limit hits | 2 |
When a limit holds a message back, the next one says how many it missed.
Emails say what happened and link to the Activity Log, or to the Other plugins tab
for new tools. They never include the
content of a call, a user name or an IP address. They go out through WordPress’s
own mail to the address you type, so on a host where mail is unreliable the
admin notice is the dependable option, and Send a test email checks the path
first. The daily email needs WP-Cron, which only runs when the site gets visits
and not at all if DISABLE_WP_CRON is set. On a quiet site, point a real cron
job at wp-cron.php. The admin notice and the email right away do not depend on
cron.
The screenshot below was taken before the fifth switch arrived in 1.11.0.
Two more switches in the same card
Section titled “Two more switches in the same card”The five optional controls at the top of this page are per-call limits on abilities that are still registered as MCP tools. Two other switches head the same Safety controls card on the Settings tab, and they work a level earlier: they decide what gets registered at all. They sit apart from those five because they do not share the “off until you set them” promise.
- Read-only mode, off by default, added in 1.6.0. One switch and nothing that writes is registered as an MCP tool, whatever you have ticked, so a blocked write is missing from the agent’s tool list rather than refused when it calls. It covers abilities bridged from your other plugins too, each judged by that plugin’s own annotation, and anything that declares neither way counts as a write and stays out. Turning it on enables nothing by itself, and turning it off enables nothing either.
- The high-risk lock, on by default, added in 1.5.0. The WooCommerce abilities that move money or grant authority stay locked even after you enable them, until you switch the high-risk control on as well. That switch is written to the audit log.
Both are covered in full on Features and Security.
Next steps
Section titled “Next steps”- Governance concepts: the always-on model underneath.
- Controlling each connection: pause, end date, per-connection rate limit, presets and Pause all access.
- Security: read-only mode and the high-risk lock in full, plus what each credential reaches.
- Get an email when an AI agent does something risky: setup, limits and mail caveats.
- Troubleshooting: common connection snags and fixes.